Job Board 2.0, and a security sweep across every Tool
Job Board 2.0 brings companies, agents and candidates together with credits, IR35 on every contract, interviews, messages, notes, reviews and testimonials. The same release hardens every Tool after a full security sweep.
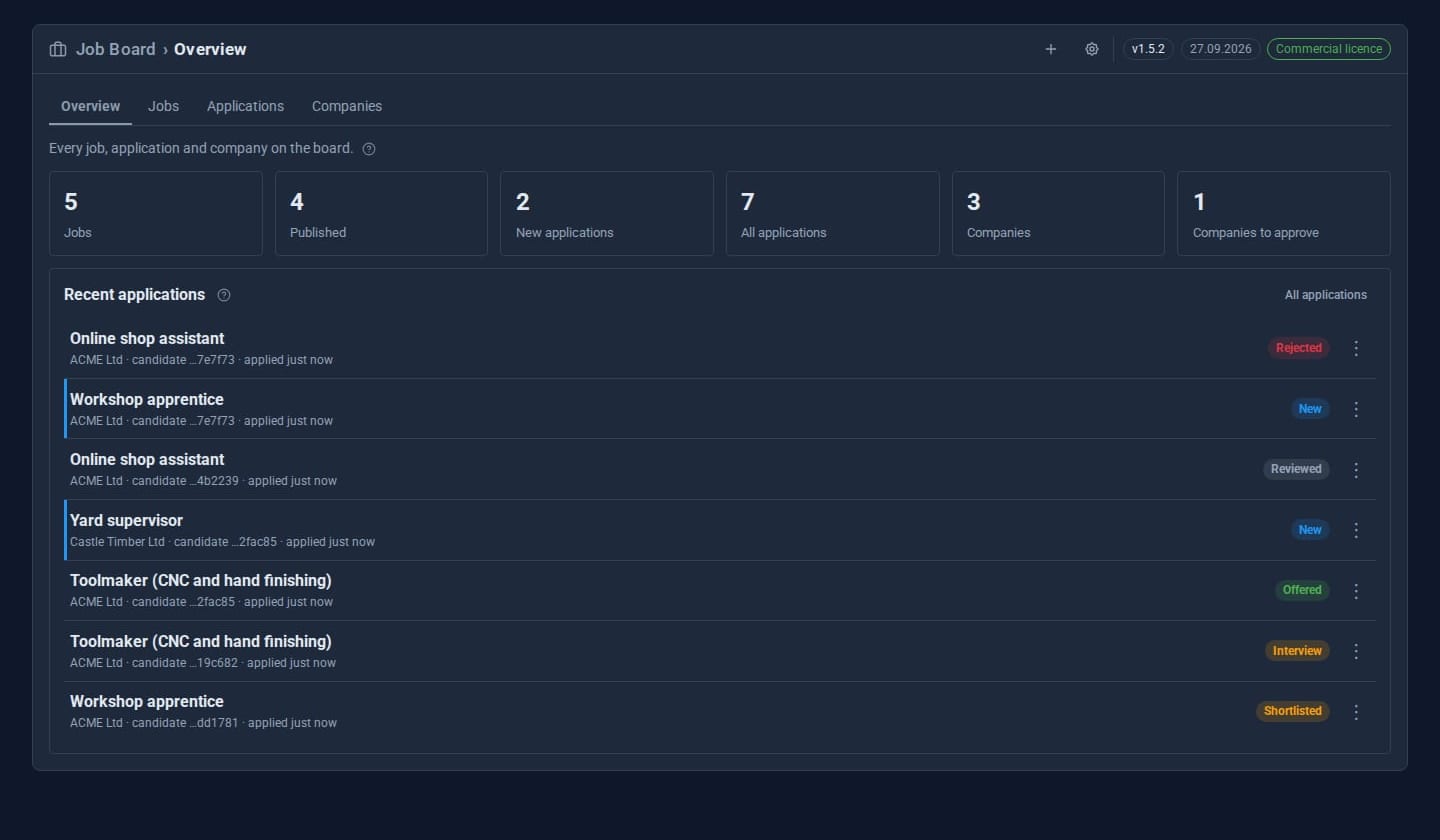
Two things went out today: a much bigger Job Board, and a security sweep across every Tool in the catalogue.
Job Board 2.0
The Job Board now runs a whole recruitment board, not just a list of vacancies.
- Three kinds of account, each with its own sign-up. Candidates and recruitment agents sign up on your site as before; now companies can too, when you switch it on, and they wait for your approval before they can publish.
- Roles and contracts carry their terms. Every role has its type (permanent, contract, fixed-term, temporary and so on) and every contract its IR35 position and status, with pay per year, day or hour, a duration and a start date. A contract cannot be published without its IR35 details.
- Credits pay for publishing. A company buys credits by card, or you gift them; a company can pass credits to an agent working for it, and agents can buy their own. A role is only ever charged once.
- Candidates have a real profile: a bio, work history, preferences (the types of role, IR35, remote or on site, locations, pay) that drive a "Matches me" filter, and testimonials - written for them by companies and agents, shown only when the candidate agrees, or added from past employers.
- Agents represent candidates. An agent invites a candidate, sees their profile and how complete it is, messages them, keeps notes and leaves a review.
- Interviews, messages, notes and reviews on every application: propose an interview and the candidate confirms or declines; message each other; the team keeps private notes and reviews that the candidate never sees.
Everything is scoped to the people it concerns - a record you have no part in simply is not there.
A security sweep of every Tool
We reviewed every Tool, the shared mail and call code, and the built-in Tools, looking for anything that could let the wrong person see or change your data. The fixes are in this release and on every managed site:
- Calendar's private events and RSVPs were readable through the generic data API. Closed on every site the same day, and the Tool now ships closed.
- A malformed browser cookie could sign a Security Pro user in without their second factor. Fixed in the Tool and in the engine, which now refuses a sign-in when a second-factor check fails for any reason.
- Blog slugs can no longer collide, link previews and link monitors cannot reach private addresses, public comment and survey forms are rate-limited, survey exports are safe to open in a spreadsheet, and emails never build links from a request's address.
- Shop account confirmation no longer reveals email addresses, Takeaway kitchen links use proper random codes, refunds cannot be sent twice, invoices cannot lose a payment while a PDF is being sent, and Cards sign-ups cannot be hijacked.
- The engine keeps every admin to their own notes, tasks and contacts, and to the Tools they have permission for, even through the data API; the request log no longer records tokens; Analytics keeps masked addresses by default.
The user manual has the updated Job Board chapter and a new Support chapter.
Keep reading
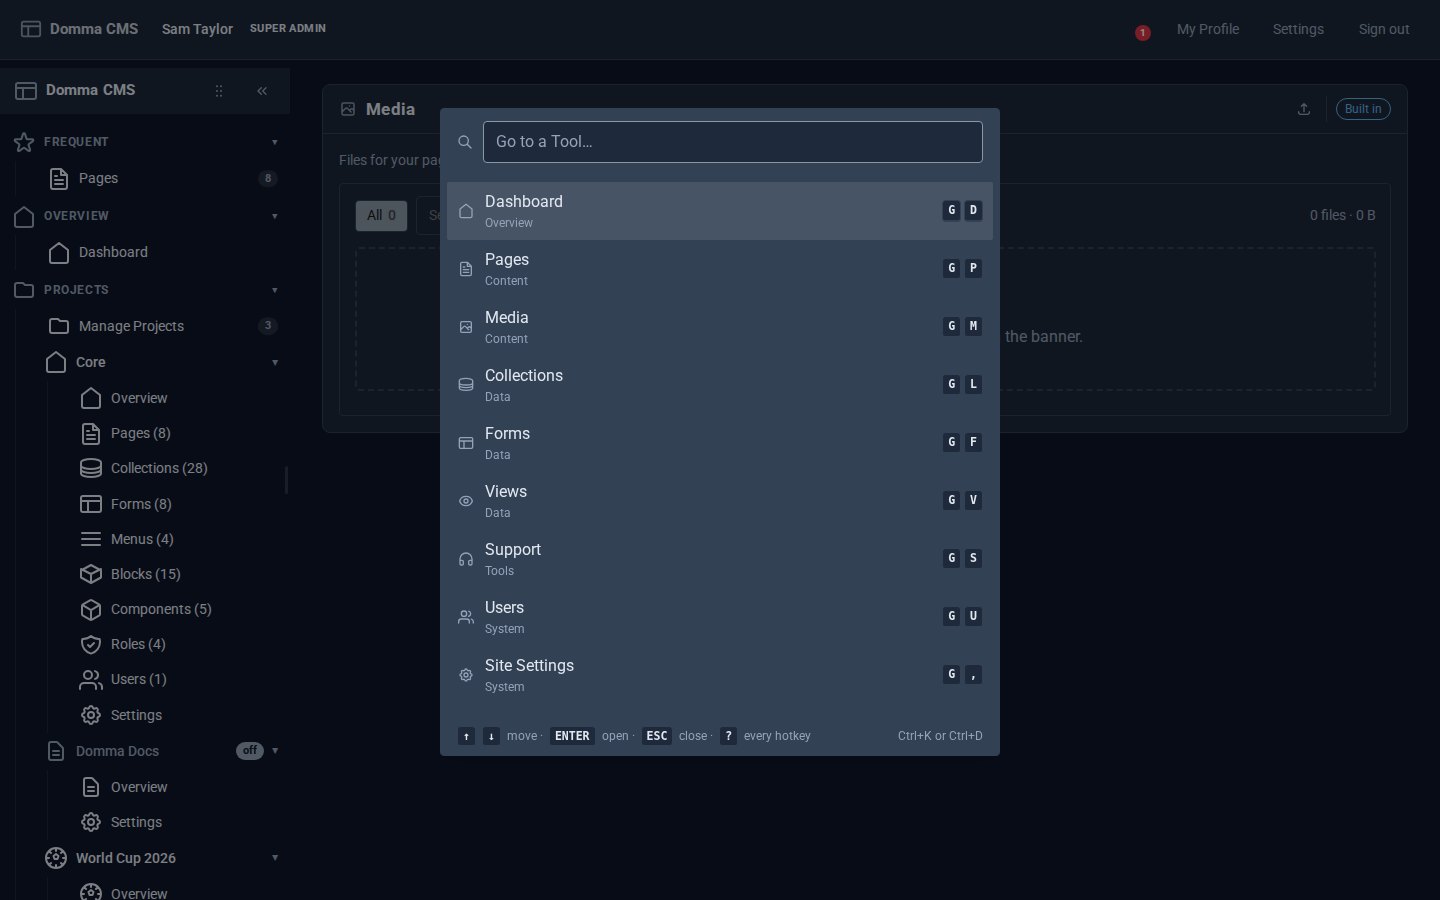
Every Tool, a keystroke away
Domma CMS 1.6: press G then a letter to open any Tool, G then 1-9 for your Frequent ones, Ctrl+K to find anything by name, and ? for the list.
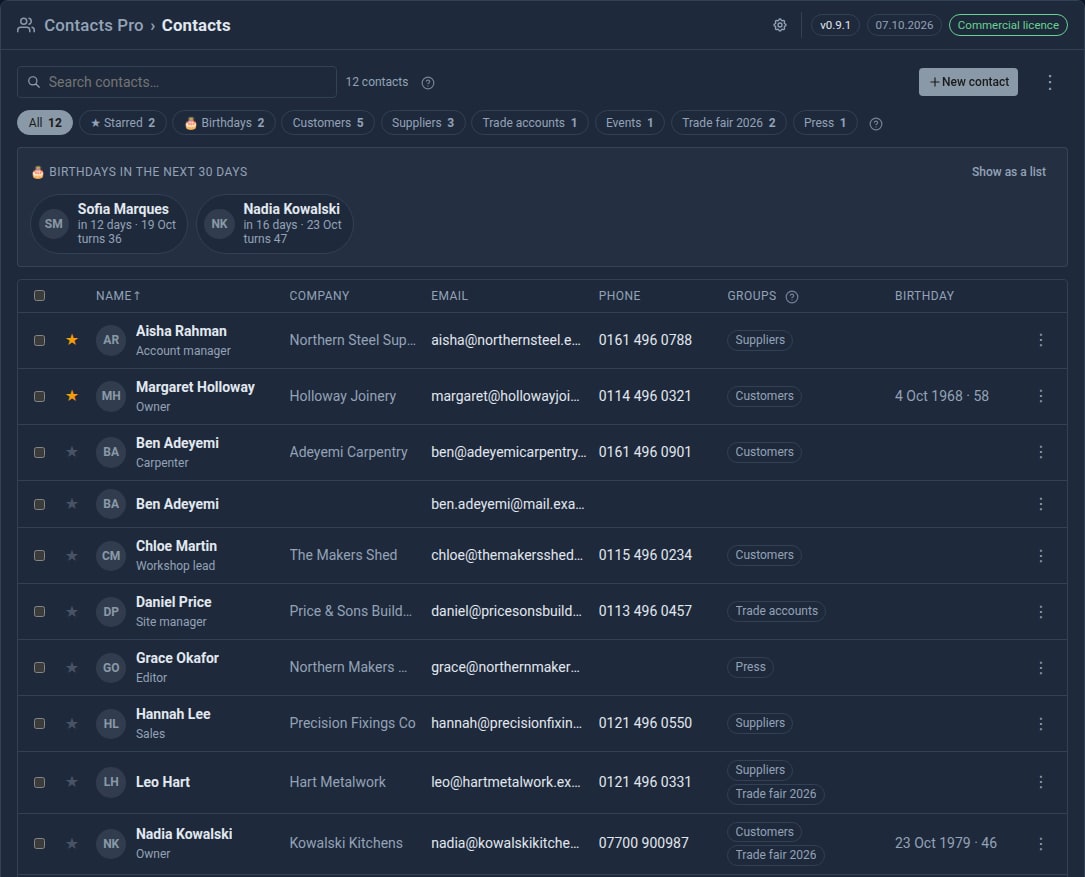
Bring your contacts in from Google
Contacts Pro 0.9 imports your address book from Google, a phone or Outlook - and merges the people you already have instead of doubling them up.
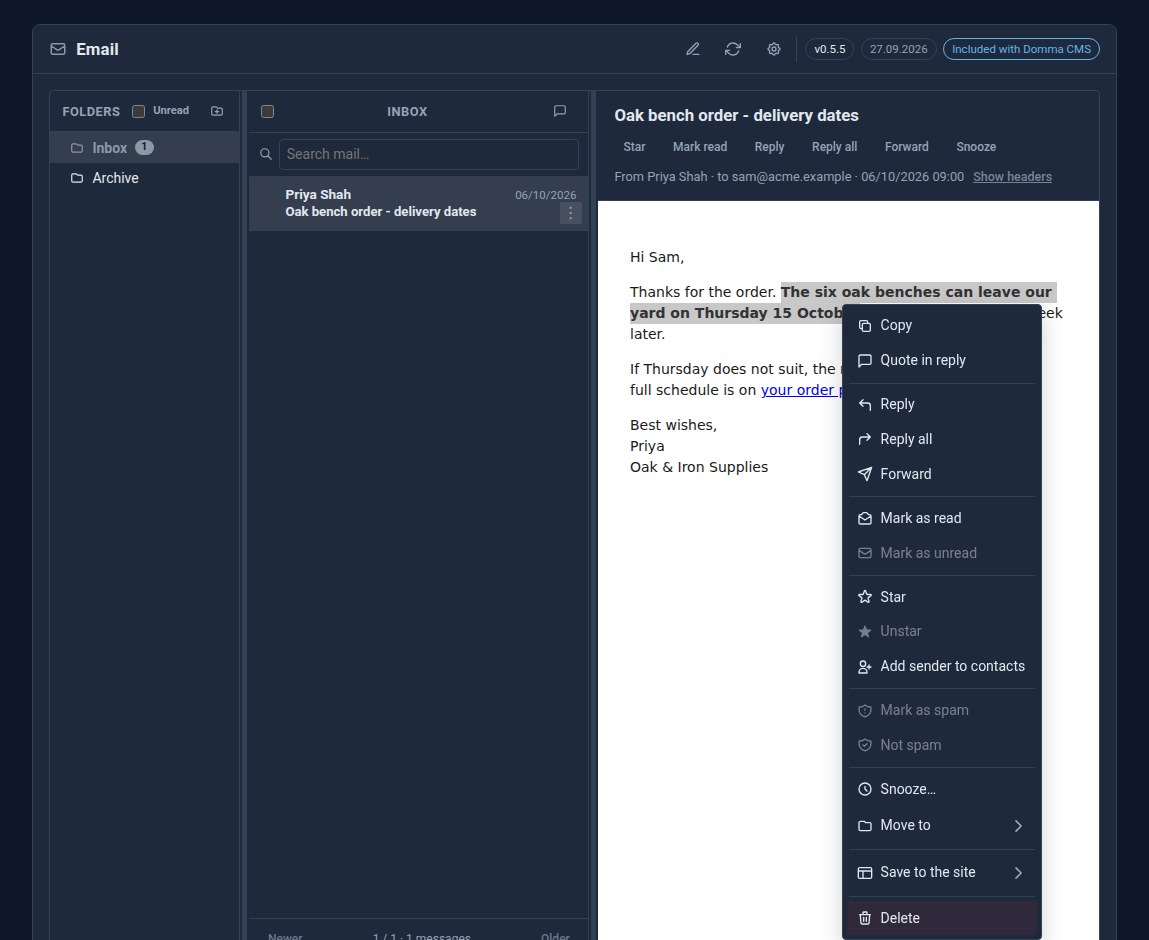
Right-click the email itself
Right-click an open email in Domma CMS for Reply, Reply all, Forward and the message's other actions - or select a sentence and quote just that in your reply.